Cyberattacks can affect businesses, hospitals, banks, government offices, and other organizations. When a security problem occurs, companies need trained professionals who can investigate the issue, limit the damage, and help restore normal operations. These professionals work in cybersecurity incident response.
If you are searching for incident response jobs, you may want to know which positions are available, what skills employers expect, and how much you can earn. You may also be wondering whether you can enter this career without years of cybersecurity experience.
The good news is that incident response offers several career paths. You can start with an entry-level security position, build technical skills, and move into specialized response roles as you gain experience.
This guide explains the main job titles, daily duties, salary information, required skills, certifications, and steps to find incident response opportunities in the United States.
What Are Incident Response Jobs?
Incident response jobs are cybersecurity positions focused on finding, investigating, containing, and recovering from security incidents. A security incident is an event that threatens the safety, privacy, or availability of computer systems, networks, or information.
These incidents may include:
- Ransomware attacks: Criminals lock files or systems and demand payment.
- Phishing attacks: Attackers use fake emails or websites to steal information.
- Malware infections: Harmful software enters a computer or network.
- Data breaches: Private or sensitive information is accessed without permission.
- Unauthorized access: Someone enters a system or account without approval.
- Network attacks: Criminals disrupt or misuse network services.
An incident response professional works with security teams to investigate these events and reduce their impact.
Example 1:
A security analyst notices unusual login activity on a company’s network. The incident response team investigates the activity, checks affected accounts, and blocks unauthorized access.
This example shows how an incident response team can help stop a possible security breach before it causes more damage.
What Is the Main Goal of Incident Response?
The main goal is to manage a security incident in a controlled way. Professionals aim to:
- Detect suspicious activity.
- Confirm whether a security incident has occurred.
- Identify affected systems and accounts.
- Contain the threat.
- Remove the cause of the incident.
- Restore affected systems safely.
- Review what happened and prevent similar incidents.
The work may involve security software, network equipment, cloud systems, digital evidence, and communication with other departments.
Common Types of Incident Response Jobs
There are several job titles in this field. The exact duties depend on the employer, team size, and level of experience.
1. Incident Response Analyst
An incident response analyst investigates security alerts and helps manage cybersecurity incidents.
Typical duties include:
- Reviewing security alerts.
- Investigating suspicious activity.
- Checking system and network logs.
- Identifying affected devices.
- Supporting threat containment.
- Writing incident reports.
- Working with other security professionals.
This role can be a good option for people who have experience in IT support, networking, or security operations.
Example 2:
An incident response analyst receives an alert about repeated failed login attempts. The analyst checks the login records, identifies the affected account, and reports the findings to the security team.
This shows how analysts use system records to investigate possible attacks.
2. Cybersecurity Incident Responder
A cybersecurity incident responder helps organizations handle confirmed security incidents.
Their responsibilities may include:
- Investigating cyberattacks.
- Containing infected devices.
- Supporting malware investigations.
- Coordinating response activities.
- Working with IT teams during recovery.
- Documenting the incident.
Some responders work directly for companies, while others work for cybersecurity consulting firms.
3. Digital Forensics Analyst
A digital forensics analyst examines computers, storage devices, logs, and other digital evidence to find out what happened during a security incident.
Common tasks include:
- Collecting digital evidence.
- Examining computer files.
- Reviewing system activity.
- Investigating malware behavior.
- Building incident timelines.
- Preparing technical reports.
This role requires strong attention to detail and knowledge of computer systems.
Example 3:
A company discovers that confidential files were copied from an employee’s computer. A digital forensics analyst examines available records to identify when the files were accessed and which systems were involved.
The investigation can help the organization find the source of the incident and protect other systems.
4. Security Operations Center (SOC) Analyst
A Security Operations Center (SOC) analyst monitors an organization’s systems for suspicious activity.
Common responsibilities include:
- Monitoring security alerts.
- Reviewing network activity.
- Investigating unusual logins.
- Checking suspicious files.
- Escalating serious incidents.
- Recording investigation results.
Many people use a SOC analyst position as a starting point for a future career in incident response.
5. Incident Response Engineer
An incident response engineer focuses on the technical side of security investigations and response operations.
Job duties may include:
- Building security monitoring systems.
- Improving incident detection.
- Creating investigation tools.
- Automating response tasks.
- Supporting cloud security investigations.
- Improving security controls.
These positions often require experience with scripting, networks, operating systems, and security platforms.
6. Incident Response Manager
An incident response manager leads a team responsible for handling cybersecurity incidents.
Typical duties include:
- Managing response teams.
- Assigning investigation tasks.
- Coordinating with company leaders.
- Reviewing incident reports.
- Managing response plans.
- Leading major incident meetings.
This position generally requires previous cybersecurity experience and strong leadership skills.
What Does an Incident Response Professional Do Every Day?
Daily tasks depend on the job title and organization. Some professionals mainly investigate alerts, while others lead full incident investigations.
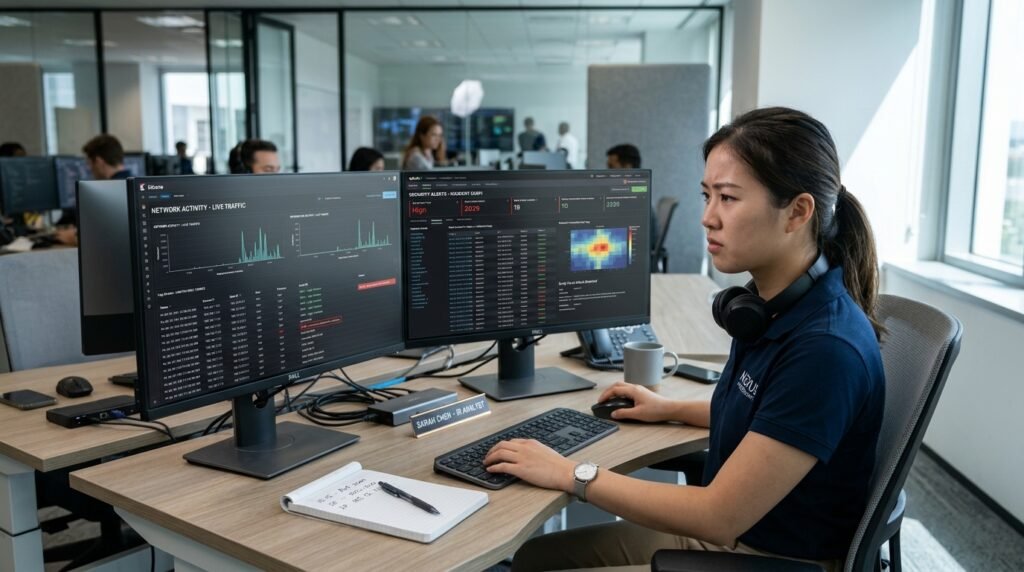
A normal workday may include:
| Daily Task | What It Involves |
|---|---|
| Security monitoring | Checking alerts and suspicious activity |
| Incident investigation | Finding out what happened |
| Log analysis | Reviewing records from systems and networks |
| Threat containment | Limiting the spread of an attack |
| Evidence collection | Saving useful digital records |
| Recovery support | Helping restore affected systems |
| Reporting | Recording findings and actions |
| Team communication | Sharing updates with IT and management |
Some incidents take only a few hours to investigate. Serious attacks may require several teams and extended response work.
Example 4:
A hospital detects suspicious activity on a computer used by its staff. The response team works with IT professionals to isolate the affected device, investigate the alert, and help protect other systems.
This example shows why communication and teamwork matter during security incidents.
Skills Needed for Incident Response Jobs
Employers look for a mix of technical and communication skills. You do not need to know every security tool before applying, but you should understand the basic systems used in cybersecurity.
1. Networking Skills
Learn how computer networks work. Study:
- TCP/IP: A group of rules that allows devices to communicate.
- DNS: A service that connects domain names with IP addresses.
- HTTP and HTTPS: Rules used for communication between web browsers and servers.
- Firewalls: Security systems that control network traffic.
- VPNs: Tools that create secure network connections.
These topics help you identify unusual network activity.
2. Operating System Knowledge
You should have basic knowledge of Windows and Linux.
Learn how to:
- Check system logs.
- Manage user accounts.
- Review running processes.
- Find unusual files.
- Use command-line tools.
- Check system settings.
3. Security Monitoring Tools
Many incident response teams use security tools to collect and review information.
Common tool categories include:
- SIEM: Security Information and Event Management platforms that collect and analyze security records.
- EDR: Endpoint Detection and Response tools that monitor computers and other devices.
- Threat intelligence platforms: Tools that provide information about known threats.
- Network monitoring tools: Software that helps review network traffic.
Examples of commonly used products include Splunk, Microsoft Sentinel, Microsoft Defender, and CrowdStrike Falcon. Employers may use different platforms, so focus on learning the main concepts rather than one product alone.
4. Digital Forensics Skills
Digital forensics involves collecting and examining digital evidence.
Useful areas to study include:
- File system analysis.
- Browser history analysis.
- System logs.
- Memory analysis.
- Malware investigation.
- Evidence handling.
5. Scripting and Automation
Basic scripting can help you complete repeated tasks faster.
Useful languages include:
- Python: Used for automation, data analysis, and security tasks.
- PowerShell: Commonly used to manage Windows systems.
- Bash: Used for command-line tasks on Linux and Unix systems.
You do not need to become an expert programmer for every incident response position. However, basic scripting can make your work easier.
6. Communication and Problem-Solving
Technical skills are only part of the job.
Incident response professionals also need to:
- Explain problems in simple language.
- Write clear incident reports.
- Share accurate updates.
- Work with different departments.
- Stay calm during serious incidents.
- Make decisions based on evidence.
Example 5:
An analyst finds that an employee account was accessed without permission. The analyst explains the risk to the IT manager, shares the available evidence, and recommends securing the account.
This shows how clear communication supports a technical investigation.
Education and Qualifications for Incident Response Jobs
There is no single education path for every incident response position. Employers set different requirements based on the work and level of responsibility.
Do You Need a College Degree?
Many employers prefer candidates with a bachelor’s degree in a related field, such as:
- Computer Science.
- Cybersecurity.
- Information Technology.
- Information Systems.
- Computer Engineering.
However, a degree is not the only way to enter cybersecurity. Some employers consider candidates with relevant technical experience, professional training, certifications, and practical skills.
A person with an IT support background may move into a SOC analyst role after gaining security knowledge.
Do You Need Previous Experience?
Experience requirements depend on the position.
Entry-level security roles may accept candidates with limited professional experience. More advanced incident response positions often require several years of work in cybersecurity, IT, networking, or digital forensics.
You can build experience through:
- IT support work.
- Network administration.
- SOC analyst positions.
- Cybersecurity internships.
- Home labs.
- Authorized cybersecurity training environments.
- Practical security projects.
Example 6:
A recent graduate creates a home lab using virtual machines. They practice reviewing Windows logs, investigating suspicious files, and writing short incident reports.
This gives the candidate practical examples to discuss during job interviews.
Best Certifications for Incident Response Jobs
Certifications can help show that you have studied important cybersecurity topics. The right choice depends on your experience and the type of role you want.
Here are some well-known options.
1. CompTIA Security+
CompTIA Security+ is a general cybersecurity certification. It covers security basics, threats, risk management, and network security.
It can be a useful starting point for people entering cybersecurity.
2. CompTIA CySA+
CompTIA CySA+ focuses on cybersecurity analysis, threat detection, and response-related skills.
It may suit people who want to work in security analysis or SOC environments.
3. GIAC Certified Incident Handler (GCIH)
The GIAC Certified Incident Handler (GCIH) certification focuses on identifying and handling security incidents.
It is relevant to professionals who want to build incident handling knowledge.
4. Certified Information Systems Security Professional (CISSP)
CISSP is an advanced cybersecurity certification covering several areas of information security.
It is more suitable for experienced professionals moving into senior security or management roles. It has specific experience requirements.
5. Certified Computer Forensics Examiner (CCFE)
The Certified Computer Forensics Examiner (CCFE) is a digital forensics credential offered by the International Association of Computer Investigative Specialists.
It may be relevant to professionals interested in computer evidence and forensic investigations. Check the current certification requirements before enrolling.
Which Certification Should You Choose?
| Your Current Level | Certification to Consider |
|---|---|
| Beginner | CompTIA Security+ |
| Security analyst | CompTIA CySA+ |
| Incident handling professional | GIAC GCIH |
| Experienced security professional | CISSP |
| Digital forensics specialist | CCFE |
Do not collect certifications without gaining practical skills. Employers also want to see that you can investigate problems and explain your findings.
Incident Response Jobs Salary in the USA
Salary is one of the main factors people consider before choosing a career.
There is no single national salary figure for all incident response jobs. Pay changes based on job title, location, experience, industry, employer, and technical skills.
The U.S. Bureau of Labor Statistics reports that the median annual wage for Information Security Analysts was $129,180 in May 2025. This is a related occupational category, not a salary figure for every incident response specialist.
The BLS also projects 21% employment growth for information security analysts from 2025 to 2035.
What Affects Incident Response Salaries?
Several factors can affect your earning potential.
Experience: Senior professionals often earn more because they handle complex investigations and major incidents.
Location: Pay can differ between cities and states. Areas with many technology and financial companies may offer different salary levels.
Technical skills: Knowledge of cloud security, digital forensics, malware analysis, and security automation may help qualify you for specialized positions.
Industry: Financial services, healthcare, government contractors, and technology companies may have different salary structures.
Job level: An entry-level SOC analyst and a senior incident response manager have different responsibilities and pay ranges.
How to Research Current Salaries
Before applying, compare job listings for the exact title you want.
Search for:
- Incident response analyst salary.
- Cybersecurity incident responder salary.
- Digital forensics analyst salary.
- SOC analyst salary.
- Incident response engineer salary.
Check whether the listed pay is an hourly rate or annual salary. Also review the location, experience requirements, and benefits.
Entry-Level Incident Response Jobs
You do not always need to start as an incident response specialist.
Many professionals begin in related IT or cybersecurity positions and move into incident response after building experience.
Best Entry-Level Positions
1. Junior SOC Analyst
Monitors security alerts and helps investigate suspicious activity.
2. Junior Cybersecurity Analyst
Supports security monitoring, risk reviews, and basic investigations.
3. IT Support Specialist
Helps users with computer, software, account, and network problems. This role can build useful technical experience.
4. Network Support Technician
Works with network devices, connections, and basic troubleshooting.
5. Security Operations Intern
Gets practical experience by supporting a security team under supervision.
How to Get Your First Job Without Experience
If you are new to cybersecurity, follow these steps:
- Learn basic computer networking.
- Study Windows and Linux.
- Learn common cybersecurity threats.
- Practice reviewing security logs.
- Study a beginner-friendly certification.
- Create a small home lab.
- Write reports about your practice investigations.
- Apply for junior SOC and security analyst roles.
Example 7:
A beginner completes a networking course, studies Security+, and practices reviewing security alerts in a home lab. They then apply for junior SOC analyst positions.
This is a realistic starting route for someone who wants to move into incident response.
Remote Incident Response Jobs
Some companies offer remote incident response jobs, allowing employees to work outside a traditional office.
Remote work depends on the employer, role, and security requirements. Some positions require office attendance or on-site support during serious incidents.
Remote responsibilities may include:
- Reviewing security alerts.
- Investigating system logs.
- Joining incident response meetings.
- Writing investigation reports.
- Supporting threat containment.
- Working with distributed security teams.
Where Can You Find Remote Opportunities?
Search job websites using terms such as:
- Remote incident response analyst.
- Remote cybersecurity analyst.
- Remote SOC analyst.
- Remote digital forensics analyst.
- Remote security operations specialist.
Read the location requirements carefully. Some jobs are remote only within the United States, while others allow applicants from specific states.
Also check whether the employer requires security clearance, background checks, or legal permission to work in the country.
Where to Find Incident Response Jobs
You can search for incident response openings through general job websites, employer career pages, and cybersecurity job boards.
Useful places to check include:
- LinkedIn Jobs: Search for cybersecurity and incident response positions.
- Indeed: Compare job titles, salary details, and experience requirements.
- Glassdoor: Review employer information and available salary reports.
- USAJOBS: Search for eligible federal government cybersecurity positions.
- Employer career pages: Check technology companies, banks, consulting firms, and security service providers.
Search Using Different Job Titles
Employers do not always use the exact phrase incident response jobs.
Try these search terms:
| Search Term | Type of Work |
|---|---|
| Incident Response Analyst | Security incident investigations |
| Cyber Incident Responder | Handling cyberattacks |
| Security Analyst | Monitoring and investigating threats |
| SOC Analyst | Security alert monitoring |
| Digital Forensics Analyst | Examining digital evidence |
| Incident Response Engineer | Technical response and automation |
| Incident Handler | Managing security incidents |
| Threat Detection Analyst | Finding suspicious activity |
Searching several related titles can help you find opportunities that a single keyword search may miss.
How to Apply for Incident Response Jobs
A strong application should show that you understand cybersecurity basics and can perform the tasks listed in the job description.
Step 1: Choose the Right Job Level
Do not apply only for senior incident response positions if you are new to cybersecurity.
Start by checking junior security analyst, SOC analyst, and internship opportunities.
Step 2: Build a Relevant Resume
Your resume should include:
- Education.
- Relevant certifications.
- Technical skills.
- IT or cybersecurity experience.
- Practical projects.
- Security tools you have used.
- Clear examples of your work.
Avoid listing tools that you have never used.
Step 3: Show Practical Projects
A practical project can help show your skills even if you have limited professional experience.
Possible projects include:
- Reviewing Windows event logs.
- Creating a basic network monitoring lab.
- Investigating a sample phishing email.
- Analyzing a safe malware training sample in an isolated lab.
- Writing a mock incident response report.
- Creating a simple Python script to organize security logs.
Only use systems and files you have permission to examine.
Step 4: Prepare for Technical Interviews
Employers may ask questions about:
- How you investigate a security alert.
- How phishing attacks work.
- What a SIEM platform does.
- How you review suspicious login activity.
- What happens during incident containment.
- How you document an investigation.
Practice explaining your answers in clear language.
Step 5: Apply and Follow Up
Apply to positions that match your current skills. Adjust your resume to show the experience and abilities mentioned in each job description.
Keep a record of applications, interview dates, and employer responses.
Career Path in Incident Response
Incident response can lead to several cybersecurity career options.
Here is one possible career path:
Entry-Level Roles
- IT Support Specialist.
- Junior SOC Analyst.
- Junior Cybersecurity Analyst.
Mid-Level Roles
- Incident Response Analyst.
- Cybersecurity Incident Responder.
- Digital Forensics Analyst.
Senior-Level Roles
- Senior Incident Response Analyst.
- Incident Response Engineer.
- Senior Digital Forensics Specialist.
Leadership Roles
- Incident Response Manager.
- Security Operations Manager.
- Director of Incident Response.
- Chief Information Security Officer (CISO).
This is only one possible path. Some people move from networking or system administration into cybersecurity, while others start in security operations.
Is Incident Response a Good Career Choice?
Incident response may suit people who enjoy solving technical problems, investigating unusual activity, and working with computer systems.
It can offer opportunities in several industries, including finance, healthcare, government, technology, and consulting.
However, the work can also be demanding. Serious incidents may require urgent action, long working hours, and communication outside normal business hours.
Before choosing this career, consider whether you enjoy technical investigations, continuous learning, teamwork, and working under pressure.
Example 8:
A security professional enjoys investigating unusual network activity and finding the reason behind security alerts. They decide to focus on incident response and begin studying digital forensics.
This is an example of how personal interests can help guide a cybersecurity career choice.
Frequently Asked Questions About Incident Response Jobs
1. What qualifications do you need for incident response jobs?
Requirements vary by employer. Many positions prefer a degree in cybersecurity, computer science, or information technology. Relevant experience, technical training, certifications, and practical projects can also help.
2. Are there entry-level incident response jobs?
Yes. Some employers offer junior incident response and security analyst positions. You can also start as a SOC analyst, IT support specialist, or security operations intern before moving into a specialized response role.
3. How much do incident response analysts make?
Pay depends on experience, location, employer, and job duties. The BLS reported a median annual wage of $129,180 for information security analysts in May 2025. This figure represents a related occupation rather than every incident response job.
4. Can I work remotely in incident response?
Yes. Some companies offer remote cybersecurity response positions. However, certain employers require office attendance, on-site support, or applicants who live in specific locations.
5. Which certification is best for incident response?
The right certification depends on your experience. CompTIA Security+ may be a useful starting point, while CySA+ and GIAC GCIH offer more focused security analysis and incident handling knowledge.
6. Do incident response professionals need coding skills?
Not every position requires advanced coding. However, basic knowledge of Python, PowerShell, or Bash can help with log analysis, automation, and technical investigations.
7. What is the difference between a SOC analyst and an incident response analyst?
A SOC analyst mainly monitors security alerts and investigates suspicious activity. An incident response analyst focuses more directly on investigating and managing confirmed or suspected security incidents. In smaller organizations, both roles may have similar duties.
8. Where can I find cybersecurity incident response jobs?
You can search on LinkedIn Jobs, Indeed, Glassdoor, USAJOBS, and company career pages. Use related job titles such as incident handler, SOC analyst, and cybersecurity incident responder.
9. Is incident response stressful?
It can be stressful, especially during major cyberattacks. Professionals may need to work quickly, communicate clearly, and help protect important systems. The workload also depends on the employer and team structure.
10. Can I get an incident response job without a degree?
Some employers consider candidates without a college degree if they have relevant technical experience, certifications, and practical skills. However, other employers have formal degree requirements, particularly for specialized or senior positions.
Conclusion
Incident response jobs offer career opportunities for people interested in cybersecurity, digital investigations, and protecting computer systems. Available positions include incident response analyst, cyber incident responder, SOC analyst, digital forensics analyst, and incident response engineer.
To get started, learn networking, Windows, Linux, and basic security concepts. Build practical experience through labs and projects, consider relevant certifications, and apply for entry-level cybersecurity positions if you have limited experience.
The best way to prepare is to combine technical knowledge with hands-on practice. Start with a role that matches your current skills, keep learning, and work toward a specialized incident response position as your experience grows.
Emily Carter (Content Writer & Communication Specialist) is a content writer and communication specialist at AllTypeInfo.com. She writes clear, practical, and easy-to-follow guides on email responses, message replies, writing templates, and everyday communication tips. Her goal is to help readers communicate with confidence in both personal and professional settings.