A cyberattack can disrupt business operations, expose private information, and cause financial losses. Whether a company faces a ransomware attack, a phishing email, or an unauthorized login, it needs a clear plan to respond.
Following the correct cyber incident response steps helps organizations control threats, protect important data, and restore affected systems. A quick and well-planned response can also limit damage and reduce the risk of another attack.
This guide explains the main stages of cyber incident response, what to do during each stage, and how businesses can prepare for future security problems. It also includes practical examples and a checklist that IT teams can use during an incident.
What Are Cyber Incident Response Steps?
Cyber incident response steps are a series of actions that an organization follows to identify, investigate, control, and recover from a cybersecurity incident.
A cybersecurity incident is an event that threatens the safety, privacy, or availability of computer systems, networks, or data. Examples include ransomware attacks, data breaches, phishing attacks, malware infections, and unauthorized access.
The main goal of an incident response process is to reduce damage, remove threats, protect information, and return business systems to normal operation.
Organizations often use guidance from the National Institute of Standards and Technology (NIST) to build their response plans. NIST published Special Publication 800-61 Revision 3 (SP 800-61 Rev. 3) in April 2025. It connects incident response with the NIST Cybersecurity Framework (CSF) 2.0 and treats response as part of ongoing cybersecurity risk management.
For practical use, businesses can organize their response activities into these six operational stages:
- Preparation
- Detection and identification
- Analysis and assessment
- Containment
- Eradication and recovery
- Post-incident review
These stages provide a useful working process. Some activities may overlap, and teams may need to return to an earlier stage if they discover new evidence.
1. Prepare for a Cybersecurity Incident
Preparation is the first stage of an effective cyber incident response plan. It involves getting people, systems, tools, and procedures ready before an attack happens.
A company should never wait until a security breach occurs to decide who will handle it.
Good preparation helps employees act quickly and gives the response team clear instructions during an emergency.
Create an Incident Response Plan
An incident response plan (IRP) explains how an organization will handle different types of cyber incidents.
A useful plan should include:
- The roles and responsibilities of the response team.
- Emergency contact details.
- Steps for reporting suspicious activity.
- Procedures for isolating affected devices.
- Rules for protecting digital evidence.
- Communication plans for employees and customers.
- Backup and recovery procedures.
- Contact information for external cybersecurity experts.
The plan should be easy to find and available even if the company’s main network is unavailable.
Build an Incident Response Team
Assign clear responsibilities to employees who may take part in an incident.
A typical team may include:
- Incident response manager: Coordinates the response and makes sure tasks are completed.
- IT security team: Investigates threats and manages affected systems.
- Network administrator: Checks network activity and controls access.
- Legal team: Reviews legal duties and possible reporting requirements.
- Management: Approves major business decisions.
- Public relations team: Handles approved messages to customers and the public.
Smaller businesses may assign several responsibilities to one person or use an outside cybersecurity service.
Prepare Security Tools and Backups
Organizations should have the right tools ready before an incident occurs.
Useful security resources include:
- Endpoint Detection and Response (EDR) software.
- Antivirus and anti-malware tools.
- Network monitoring systems.
- Centralized security logs.
- Multi-factor authentication (MFA).
- Secure backup systems.
- Vulnerability scanning tools.
- A reliable way to contact the response team.
Keep backups separate from everyday business systems. Test them regularly to make sure the data can be restored.
Example 1:
A small online store creates an incident response plan, assigns an IT employee to investigate security alerts, and stores daily backups in a separate protected location.
This preparation gives the store a clear process to follow if an attacker compromises its website or business systems.
2. Detect and Identify the Cyber Incident
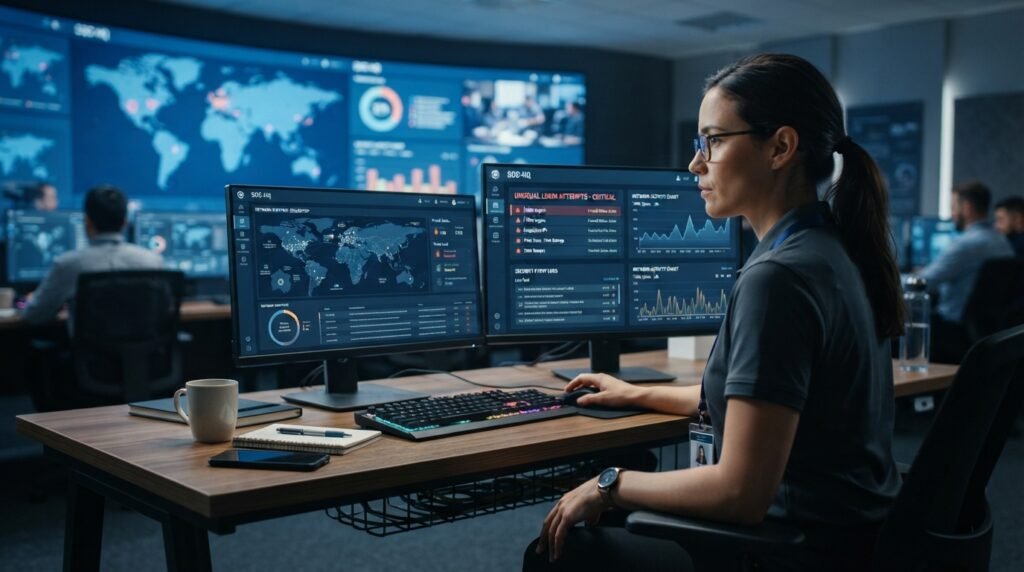
The second stage is detection and identification. The goal is to recognize suspicious activity and decide whether it may be a real security incident.
Some attacks are easy to notice, while others remain hidden for weeks or months.
Businesses should monitor their systems for unusual behavior and make it easy for employees to report possible threats.
Common Signs of a Cyber Incident
Watch for these warning signs:
- Unexpected login attempts.
- Unknown devices connected to the company network.
- Files that suddenly become encrypted.
- Unusual network traffic.
- Unexpected changes to user accounts.
- Missing or altered business files.
- Antivirus warnings.
- Unknown software installed on company computers.
- Emails sent from employee accounts without permission.
- Customers reporting suspicious activity on their accounts.
One warning sign does not always mean an attack has happened. The response team should investigate before deciding what action to take.
Common Sources of Security Alerts
Organizations can use several sources to detect possible incidents.
1. Security logs
Logs record activity on computers, servers, applications, and networks. They can help identify unusual logins, failed access attempts, and unexpected changes.
2. Endpoint security tools
EDR and antivirus software can detect suspicious programs, malware, and unusual activity on employee devices.
3. Network monitoring
Network monitoring tools help security teams find unexpected connections, unusual data transfers, and suspicious communication between devices.
4. Employee reports
Employees may notice strange emails, unexpected pop-ups, or unusual account activity before automated tools detect a problem.
Example 2:
An employee receives an email that appears to come from the company’s payroll department. After clicking the attachment, the employee notices that the computer is running unusually slowly and several security warnings appear.
The employee reports the issue to IT instead of opening more attachments. The security team investigates the device to determine whether it contains malware.
Confirm Whether an Incident Has Occurred
After receiving an alert, the response team should check whether the activity is malicious, accidental, or harmless.
For example, several failed login attempts may indicate a brute-force attack, but they could also result from an employee entering an incorrect password.
The team should record:
- When the activity started.
- Which device or account was involved.
- What systems may be affected.
- What type of suspicious activity occurred.
- Which alerts or reports revealed the problem.
- Whether the activity is still happening.
If the team confirms a security incident, it should assign a severity level and begin the appropriate response.
3. Analyze and Assess the Incident
Once a possible incident has been identified, the team needs to investigate what happened and determine how serious it is.
Incident analysis helps security professionals find the source of an attack, identify affected systems, and estimate the possible damage.
Without proper analysis, a company may respond to the wrong problem or overlook other affected devices.
Determine the Type of Cyberattack
Start by identifying the likely type of incident.
Common cybersecurity incidents include:
- Ransomware: Malware that locks or encrypts files and may demand payment.
- Phishing: Fraudulent messages designed to steal information or trick users into taking unsafe actions.
- Malware infection: Harmful software installed on a computer or network.
- Data breach: Unauthorized access to private or protected information.
- Account compromise: An attacker gains access to a legitimate user account.
- Denial-of-Service (DoS) attack: An attack that makes a website or service unavailable to users.
- Insider threat: A security risk caused by someone with authorized access, either intentionally or by mistake.
Identifying the attack type helps the team choose suitable containment and recovery actions.
Find the Scope of the Attack
The team should find out how far the incident has spread.
Check:
- Affected computers and servers.
- Compromised user accounts.
- Business applications.
- Cloud services.
- Network connections.
- Customer or employee information.
- Connected third-party systems.
Do not assume that the first affected computer is the only compromised device.
Preserve Digital Evidence
Digital evidence can help investigators determine how an attack happened and what information was affected.
Important evidence may include:
- System and application logs.
- Email headers and suspicious attachments.
- Network traffic records.
- Security alerts.
- File timestamps.
- Login records.
- Malware samples, when collected safely.
- Screenshots of relevant alerts.
Record what was collected, when it was collected, and who handled it. This helps protect the chain of custody, which is the documented record of how evidence was collected and managed.
Avoid deleting files, wiping devices, or reinstalling systems before evidence has been preserved, unless an urgent safety or business need requires immediate action. Qualified responders should guide these decisions.
Assign an Incident Severity Level
A severity rating helps management decide how quickly to respond and which resources are needed.
| Severity | Example | Suggested Response |
|---|---|---|
| Low | A blocked phishing email with no signs of compromise | Record and monitor |
| Medium | One employee account has suspicious login activity | Investigate and secure the account |
| High | Malware affects several business computers | Activate the response team and contain affected devices |
| Critical | Ransomware affects important servers or a major data breach occurs | Activate emergency procedures and senior management support |
Each organization should define its own severity rules based on business risk.
Example 3:
A company notices that an employee account has logged in from an unfamiliar location. The security team checks login records and finds that the account accessed files outside the employee’s normal work duties.
The team classifies the event as a high-priority incident, investigates the account, and checks whether other systems were accessed.
4. Contain the Cyber Incident
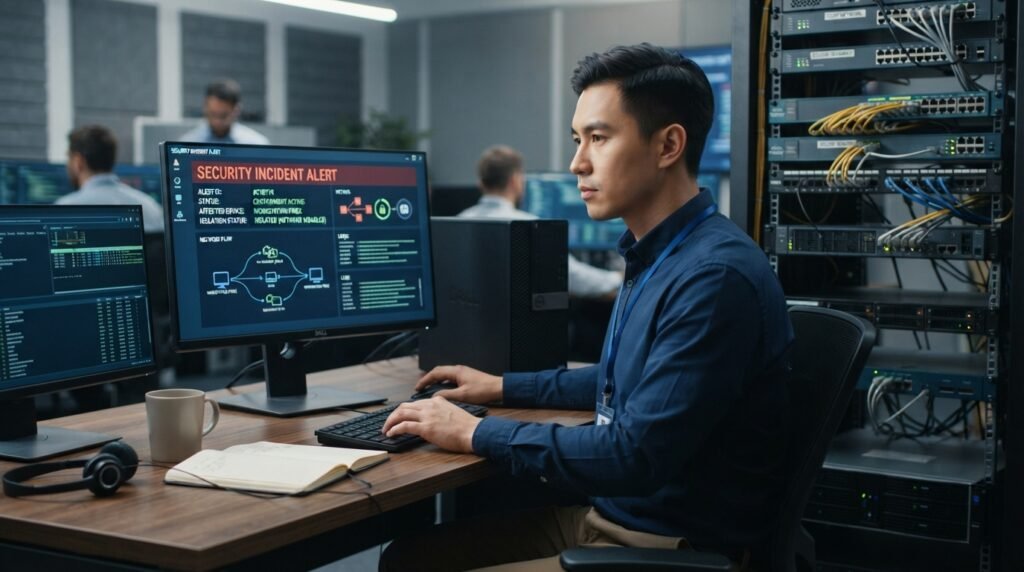
Containment means taking action to stop an attack from spreading or causing more damage.
It is one of the most important stages of incident response because attackers may continue accessing systems while the investigation is taking place.
The right action depends on the type and size of the incident.
Isolate Affected Devices
If a computer is infected with malware, the security team may disconnect it from the company network.
This can prevent the infected device from communicating with other systems.
However, isolation should be planned carefully. Disconnecting a device may affect evidence collection or business operations.
For serious incidents, qualified security professionals should decide how to isolate affected systems.
Disable Compromised Accounts
If an attacker gains access to an employee account, the response team may need to:
- Disable the compromised account.
- Revoke active login sessions.
- Reset the affected password.
- Review account permissions.
- Check for unauthorized MFA changes.
- Remove unknown recovery methods.
- Secure connected applications.
Changing a password alone may not be enough if an attacker has created another way to access the account.
Block Malicious Network Activity
Security teams can use firewalls and network controls to block suspicious connections.
They may also restrict access to affected services, block known malicious IP addresses, and disable unsafe connections.
These actions should be based on investigation results to avoid blocking legitimate business traffic.
Protect Important Systems
Some systems may need extra protection during an incident.
For example, a business may temporarily restrict access to:
- Customer databases.
- Financial systems.
- Cloud storage.
- Administrative accounts.
- Backup servers.
- Business email services.
The response team should also check whether the attacker has access to backup systems.
Example 4:
A company discovers that ransomware is spreading across several office computers. Its security team isolates the affected devices from the network and temporarily blocks suspicious connections.
These actions help limit the spread while the team investigates the attack and prepares a removal plan.
5. Eradicate the Threat
After containment, the organization must remove the attacker’s access and eliminate the cause of the incident.
This stage is called eradication.
Simply removing one infected file may not solve the problem. Attackers may leave hidden malware, stolen credentials, or unauthorized access methods behind.
Remove Malware and Malicious Files
Security professionals should inspect affected systems and remove harmful software.
Depending on the incident, they may need to:
- Remove malicious programs.
- Delete unauthorized files.
- Reinstall affected software.
- Rebuild compromised computers.
- Restore clean system configurations.
- Check for hidden access methods.
For serious malware infections, rebuilding a system from a trusted source may be safer than trying to repair it.
Fix the Security Weakness
Find and correct the weakness that allowed the attacker to enter.
Possible actions include:
- Installing security patches.
- Updating outdated software.
- Closing exposed network services.
- Fixing unsafe website settings.
- Changing compromised passwords.
- Replacing stolen security keys.
- Removing unnecessary administrator access.
- Improving MFA protection.
Check for Hidden Access
Attackers may create additional ways to return after the first infection is removed.
The security team should look for:
- Unknown administrator accounts.
- Unauthorized remote access tools.
- Suspicious scheduled tasks.
- Modified system settings.
- Unknown applications.
- Unusual login methods.
- Unauthorized changes to cloud permissions.
Example 5:
An attacker gains access to a company’s server through an outdated application. The IT team removes the malicious files, updates the application, resets compromised credentials, and checks for unauthorized accounts.
This reduces the chance that the attacker can use the same weakness again.
6. Recover Affected Systems and Business Operations
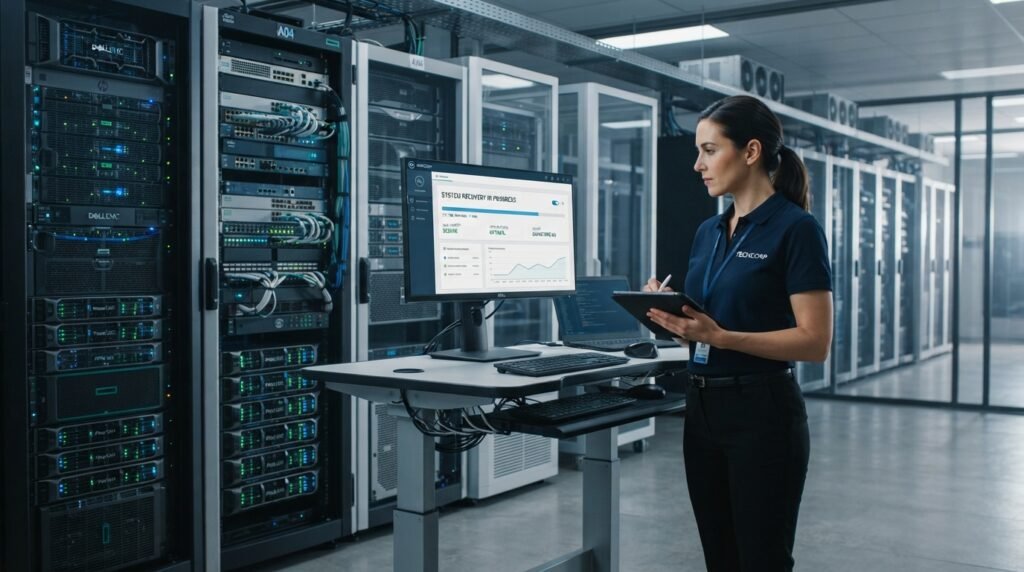
Recovery means safely returning affected systems, applications, and business services to normal operation.
A company should not rush to reconnect systems before confirming that the threat has been removed.
An incomplete recovery can allow attackers or malware to return.
Restore Data From Clean Backups
Use backups that were created before the incident and have been checked for malware or unauthorized changes.
Before restoring data:
- Confirm that the backup is clean.
- Check whether the backup system was affected.
- Select a suitable recovery point.
- Restore the required files and systems.
- Test the restored information.
- Confirm that important business functions work correctly.
Keep a separate copy of important backups whenever possible.
Test Recovered Systems
Before returning systems to normal use, check that:
- Security software is working.
- Important applications open correctly.
- User accounts are secure.
- Network connections are safe.
- Business data is complete.
- Backups can be accessed.
- No suspicious activity remains.
Monitor recovered systems for signs of another attack.
Restore Business Services in Order of Priority
Not every system needs to return online at the same time.
Organizations should restore services based on business needs.
For example:
- Essential network and security services.
- Important business applications.
- Customer-facing services.
- Internal employee systems.
- Less urgent applications.
The order should follow the company’s business continuity plan and recovery priorities.
Communicate With Employees and Customers
If the incident affects customers or employees, provide clear and accurate updates.
Messages should explain:
- What happened, based on confirmed facts.
- Which services are affected.
- What users should do.
- Whether any action is required.
- Where to get further updates.
For a suspected data breach, involve legal and privacy professionals before making public statements. Reporting duties and deadlines depend on the type of data, the location of affected people, and applicable laws.
Example 6:
A retail company restores its customer service system from a clean backup after removing ransomware from its servers. The IT team tests the system, checks customer records, and monitors activity before allowing employees to use it again.
This careful process helps the company return to normal operations without bringing the original threat back.
7. Conduct a Post-Incident Review
The response process should continue after the immediate threat has been handled.
A post-incident review helps an organization find out what happened, how the response team performed, and what needs to change.
It also helps prevent similar incidents in the future.
Identify the Root Cause
A root cause analysis looks for the main reason an incident occurred.
For example, a ransomware attack may have started because an employee opened a harmful attachment. The investigation may also find that the company had outdated software and weak access controls.
The review should identify both the initial entry point and any weaknesses that allowed the attack to spread.
Review the Response Process
Discuss questions such as:
- How quickly was the incident detected?
- Did employees report it correctly?
- Were the right people contacted?
- Was the affected system contained in time?
- Was important evidence preserved?
- Were recovery steps successful?
- Did communication work as planned?
- Which actions caused delays?
Focus on improving the process instead of blaming individuals.
Update the Incident Response Plan
Use the findings to improve the organization’s security procedures.
Possible improvements include:
- Better employee security training.
- Stronger password rules.
- More frequent backup testing.
- Improved network monitoring.
- Faster security alert notifications.
- Updated incident response contacts.
- Better access controls.
- More regular response exercises.
Example 7:
After a phishing attack, a company finds that several employees could not recognize the warning signs in a fake email. Management adds practical phishing training and improves email security controls.
The review helps the company address the weakness that contributed to the incident.
Common Types of Cyber Incidents and How to Respond
Different attacks require different actions. The following table explains common incidents and the first steps a response team may take.
| Cyber Incident | Common Warning Sign | Initial Response |
|---|---|---|
| Ransomware | Files become encrypted or inaccessible | Isolate affected systems and protect backups |
| Phishing | Suspicious emails or harmful links | Report the message and investigate affected accounts |
| Malware | Unknown software or unusual device activity | Isolate the device and investigate the infection |
| Data breach | Unauthorized access to private information | Restrict access and assess exposed data |
| Account compromise | Unknown logins or account changes | Secure the account and revoke active sessions |
| DDoS attack | Website or service becomes unavailable | Activate network protection and service continuity measures |
| Insider threat | Unusual activity by an authorized user | Preserve evidence and review access permissions |
These are general response actions. The exact process depends on the incident, the affected systems, and the organization’s security policies.
Cyber Incident Response Checklist
A checklist helps employees and IT teams follow the right actions during a stressful security event.
Use the following list as a starting point for your organization’s incident response plan.
Before an Incident
- Create a written incident response plan.
- Assign incident response team members.
- Save emergency contact details.
- Install and update security software.
- Enable multi-factor authentication.
- Store backups securely.
- Test backup restoration.
- Train employees to report suspicious activity.
- Test the response plan with practice exercises.
During an Incident
- Record the date and time of discovery.
- Report the incident to the response team.
- Identify the affected devices and accounts.
- Assess the severity of the incident.
- Preserve relevant digital evidence.
- Contain affected systems.
- Secure compromised accounts.
- Investigate the source and scope.
- Notify the correct internal teams.
- Follow legal and reporting requirements.
After an Incident
- Remove malware and unauthorized access.
- Fix the security weakness.
- Restore systems from clean backups.
- Test recovered services.
- Monitor systems for further threats.
- Communicate with affected parties when required.
- Complete a post-incident review.
- Update the incident response plan.
- Provide additional employee training.
Best Practices for Effective Cyber Incident Response
A good incident response plan needs regular attention. These practices can help businesses improve their response process.
1. Keep the Response Plan Updated
Review contact details, system information, and response procedures regularly. Update the plan whenever the organization changes its software, network, or business operations.
2. Train Employees Regularly
Employees should know how to report suspicious emails, unusual computer activity, and possible data exposure.
Short training sessions and practice exercises can help employees respond correctly.
3. Test Backups
A backup is useful only if the organization can restore it. Test backup recovery at regular intervals and keep important copies protected from unauthorized access.
4. Monitor Systems Continuously
Use security monitoring tools to identify unusual activity. Review important alerts and make sure someone is responsible for investigating them.
5. Limit User Permissions
Give employees access only to the systems and information they need for their jobs. This is known as the principle of least privilege.
It can reduce the damage an attacker causes if an account is compromised.
6. Prepare Communication Plans
Decide how the organization will contact employees, customers, service providers, and other affected parties.
Keep alternative communication methods available in case email or company messaging systems stop working.
7. Practice Different Attack Scenarios
Run exercises based on realistic situations, such as ransomware, phishing, stolen credentials, and data breaches.
These exercises help teams find gaps in their response plans before a real incident occurs.
Frequently Asked Questions About Cyber Incident Response Steps
1. What are the six cyber incident response steps?
The six common operational steps are preparation, detection and identification, analysis and assessment, containment, eradication and recovery, and post-incident review.
These steps help organizations prepare for attacks, identify threats, limit damage, restore systems, and improve future security.
2. What is the first step in cyber incident response?
The first step is preparation. Organizations should create an incident response plan, assign team responsibilities, prepare security tools, protect backups, and train employees before an attack occurs.
3. What are the four main phases of the traditional NIST incident response life cycle?
The traditional model in NIST SP 800-61 Revision 2 used four main phases:
- Preparation
- Detection and analysis
- Containment, eradication, and recovery
- Post-incident activity
NIST published Revision 3 in April 2025. The newer publication connects incident response with the six functions of the NIST Cybersecurity Framework 2.0.
4. What is the difference between containment and eradication?
Containment stops an attack from spreading or causing further damage. Eradication removes the threat and fixes the security weaknesses that allowed the attack to happen.
For example, disconnecting an infected computer from a network is containment. Removing malware and closing the weakness that allowed it to enter are eradication activities.
5. How long does cyber incident response take?
The time depends on the type and severity of the attack. A small malware incident may be handled relatively quickly, while a major ransomware attack or data breach may require days, weeks, or longer.
Investigation, legal review, system recovery, and monitoring can extend the response period.
6. Who is responsible for cyber incident response?
Responsibility is usually shared by an incident response team. This team may include IT security professionals, network administrators, management, legal staff, and communication specialists.
Smaller companies may use an outside cybersecurity provider to support their internal team.
7. What should a company do immediately after detecting a cyberattack?
The company should report the incident to its response team, record what happened, identify affected systems, and assess the risk. It should then take suitable containment actions while preserving important evidence.
For serious incidents, the company should involve qualified cybersecurity professionals.
8. Why is a cyber incident response plan important?
An incident response plan gives employees clear instructions during a security emergency. It helps organizations coordinate their response, limit damage, protect data, restore services, and meet applicable reporting duties.
Without a plan, teams may lose time deciding who should act and what steps to take.
9. What tools are used for cyber incident response?
Common tools include Endpoint Detection and Response (EDR) software, antivirus programs, firewalls, security information and event management (SIEM) systems, network monitoring tools, vulnerability scanners, and backup solutions.
The right tools depend on the organization’s size, systems, budget, and security needs.
10. What happens after a cyber incident is resolved?
The organization conducts a post-incident review. It investigates the root cause, reviews the response, checks for remaining risks, updates security controls, and improves employee training.
The goal is to reduce the chance of a similar incident happening again.
Conclusion
Following the correct cyber incident response steps helps businesses manage security incidents in a clear and organized way. The process starts with preparation and continues through detection, analysis, containment, eradication, recovery, and review.
Every organization should have a written incident response plan, secure backups, trained employees, and a team that knows what to do during an emergency.
The best time to prepare for a cyberattack is before one happens. Review your response plan, test your recovery process, and fix security weaknesses regularly to keep your business better protected.
Emily Carter (Content Writer & Communication Specialist) is a content writer and communication specialist at AllTypeInfo.com. She writes clear, practical, and easy-to-follow guides on email responses, message replies, writing templates, and everyday communication tips. Her goal is to help readers communicate with confidence in both personal and professional settings.