A cybersecurity incident can affect business operations, customer information, company systems, and employee accounts. After a security event, organizations need a clear record of what happened, how the team responded, and what steps were taken to prevent another incident.
A cybersecurity incident response report helps document these details in one place. It gives IT teams, security managers, business owners, and other stakeholders a record they can review.
In this guide, you will find a complete cybersecurity incident response report example, a practical ransomware incident sample, a step-by-step reporting process, and a reusable report template. You will also learn what information to include and which mistakes to avoid.
What Is a Cybersecurity Incident Response Report?
A cybersecurity incident response report is a formal document that records the details of a security incident and the actions taken to handle it.
It explains what happened, when the event was detected, which systems were affected, and how the organization responded. It also records the investigation results, business impact, recovery steps, and actions needed to reduce future risks.
Common incidents documented in these reports include:
- Phishing attacks: Fraudulent emails or messages that try to steal information.
- Ransomware attacks: Malware that locks files or systems and demands payment.
- Data breaches: Events involving unauthorized access to private or sensitive information.
- Malware infections: Harmful software installed on computers or servers.
- Unauthorized access: Someone accessing an account, system, or network without permission.
- Denial-of-service attacks: Attacks that make websites or online services unavailable.
- Insider threats: Security incidents caused by employees, contractors, or other trusted users.
Example 1:
An employee opens a fake invoice attachment. The file installs malware on the employee’s computer and creates unusual network activity. The IT security team investigates the event and prepares a cybersecurity incident response report.
This report records how the malware entered the computer, which systems were affected, what the security team did, and whether any company information was exposed.
Why Is a Cybersecurity Incident Response Report Important?
A well-written report gives an organization a clear record of a security event. It also helps security teams review their response and decide what needs to change.
Here are the main reasons organizations prepare these reports.
1. Creates a Clear Record of the Incident
A report records the incident’s date, time, type, affected systems, and response actions.
Without written records, important details may be lost. Team members may also give different versions of what happened.
Example 2:
A company discovers that an employee account was accessed from an unfamiliar location. The security team records the login time, affected account, suspicious activity, and actions taken to secure the account.
This creates a reliable record that other authorized team members can review.
2. Helps Find the Root Cause
The root cause is the main reason an incident happened.
For example, a ransomware attack may start because an employee opened a harmful attachment. Another incident may result from an outdated application or a stolen password.
The report helps identify the weakness that allowed the event to occur.
3. Measures Business Impact
A cybersecurity incident can interrupt daily work, affect customers, or cause financial losses.
A report should explain:
- Which departments were affected.
- Which systems stopped working.
- Whether customer or employee information was exposed.
- How long the interruption lasted.
- Whether the organization faced recovery costs.
- Whether customers or business partners were affected.
4. Supports Future Security Improvements
The report helps the organization identify weaknesses and assign actions to prevent similar incidents.
These actions may include:
- Updating software.
- Improving email security.
- Enabling multi-factor authentication (MFA).
- Training employees.
- Reviewing access permissions.
- Improving system backups.
- Adding better security monitoring.
5. Supports Internal and External Reporting
Organizations may need to share incident details with senior management, customers, insurers, regulators, legal teams, or law enforcement.
A report gives authorized people a consistent record of the event. However, legal reporting duties and deadlines depend on the type of incident, the information involved, and the laws that apply.
What Should a Cybersecurity Incident Response Report Include?
A complete security incident report should contain enough information for someone who was not involved in the investigation to understand what happened.
The following sections are useful for most organizations.
1. Incident Identification Details
Start with basic information that identifies the security event.
Include:
- Incident ID: A unique tracking number.
- Incident title: A short name for the event.
- Incident type: Phishing, ransomware, malware, data breach, or another category.
- Date and time detected: When the security team discovered the event.
- Date and time reported: When someone reported it.
- Incident status: Open, investigating, contained, resolved, or closed.
- Severity level: Critical, high, medium, or low.
- Report author: Name and role of the person preparing the report.
- Incident manager: Person responsible for coordinating the response.
Example 3:
Incident ID: SEC-2026-014
Incident Type: Ransomware
Date Detected: October 28, 2026, at 9:15 AM ET
Severity: High
Status: Contained
Report Author: IT Security Manager
This information helps the organization identify and track the incident.
2. Executive Summary
The executive summary gives a short explanation of the incident. It should help managers understand the event without reading every technical detail.
Include:
- What happened.
- How the incident was detected.
- Which systems were affected.
- The main business impact.
- What the response team did.
- The current situation.
Keep this section short and direct.
Example 4:
On October 28, 2026, the security team detected ransomware activity on an employee workstation. The incident began after an employee opened a suspicious email attachment. The affected computer was disconnected from the company network, and the security team started an investigation. No evidence of unauthorized access to customer databases was found during the initial review. The affected workstation was restored from a verified backup.
This summary gives management a clear picture of the event.
3. Incident Description
This section explains what happened in more detail.
Describe the event in the order it occurred. Include the suspicious activity, systems involved, and how the team first noticed the problem.
Avoid guesses. If the investigation has not confirmed something, clearly label it as unknown or unconfirmed.
Example 5:
An employee in the finance department received an email that appeared to contain an invoice from a business supplier. The employee opened the attachment at approximately 9:05 AM ET. Shortly afterward, endpoint security software detected unusual file activity and generated an alert.
This description explains how the incident started and how the security team became aware of it.
4. Affected Systems and Assets
List all devices, accounts, applications, networks, and services involved in the incident.
| Asset | Asset Details | Impact |
|---|---|---|
| Employee workstation | FIN-PC-014 | Ransomware activity detected |
| Finance user account | finance.user01 | Password reset required |
| Company email | Microsoft 365 | Suspicious email received |
| File server | FILE-SRV-02 | No confirmed impact |
| Customer database | CUSTOMER-DB-01 | No unauthorized access found during initial review |
Include technical details when relevant, such as:
- Hostname
- IP address
- Device type and operating system
- Account name or ID
- Application name
- Network location
- Asset owner
Do not include unnecessary personal information in a report that will be shared widely.
5. Incident Timeline
The incident timeline records important events from detection to recovery.
Use exact dates and times whenever possible. Include the correct time zone so different teams can compare records accurately.
| Date and Time (ET) | Event | Action Taken |
|---|---|---|
| Oct. 28, 9:05 AM | Employee opened a suspicious attachment | Activity flagged for review |
| Oct. 28, 9:15 AM | Security software generated an alert | Security team notified |
| Oct. 28, 9:22 AM | Ransomware activity confirmed | Investigation started |
| Oct. 28, 9:30 AM | Workstation disconnected from network | Spread risk reduced |
| Oct. 28, 10:15 AM | Initial investigation completed | Affected asset identified |
| Oct. 28, 12:00 PM | Malware removed | System prepared for recovery |
| Oct. 28, 2:30 PM | Verified backup restored | Workstation returned to service |
Example 6:
At 9:30 AM ET, the IT team disconnected FIN-PC-014 from the company network after confirming suspicious file activity.
This entry gives a clear record of the action and its timing.
6. Severity Level and Risk Assessment
The severity level shows how serious the incident is and how urgently the organization needs to respond.
Organizations should use their own incident classification policy. A simple example is:
| Severity | Meaning | Example |
|---|---|---|
| Critical | Severe impact on important systems or operations | Ransomware affecting several business-critical servers |
| High | Major impact on a system, department, or sensitive information | Confirmed compromise of an important employee account |
| Medium | Limited impact that requires investigation and action | Malware detected on one workstation |
| Low | Minor security event with limited impact | Blocked phishing attempt with no account compromise |
The security team should assess:
- Confidentiality: Was private information exposed?
- Integrity: Were files or records changed without permission?
- Availability: Were systems or services unavailable?
- Business impact: Did the incident interrupt normal operations?
- Recoverability: How difficult is it to restore affected systems?
Example 7:
The security team classified the ransomware event as High because one employee workstation was affected and normal work was interrupted. The initial investigation found no confirmed access to the customer database.
The report should explain why a severity level was selected instead of simply assigning a label.
7. Root Cause Analysis
A root cause analysis explains why the incident happened.
The security team should examine the evidence and identify the weakness that allowed the event to occur.
Possible causes include:
- A phishing email.
- A weak or reused password.
- Missing software updates.
- Incorrect system settings.
- A vulnerable application.
- Excessive user permissions.
- Poor access controls.
- An exposed remote access service.
Separate confirmed findings from possible causes.
Example 8:
The investigation found that the employee opened a malicious email attachment. The attachment launched an unauthorized program on the workstation. The investigation also found that the employee’s account did not have multi-factor authentication enabled.
This finding gives the organization two areas to review: email protection and account security.
8. Containment Actions
Containment means taking immediate steps to stop an incident from spreading or causing more damage.
Common containment actions include:
- Disconnecting infected computers from the network.
- Disabling compromised user accounts.
- Blocking harmful IP addresses and domains.
- Removing suspicious email messages.
- Restricting access to affected systems.
- Isolating affected servers.
- Preserving relevant security logs and evidence.
The team should record who performed each action and when it happened.
Example 9:
The security team disconnected FIN-PC-014 from the company network at 9:30 AM ET. The finance user’s password was reset, and the suspicious email was removed from other employee inboxes.
These actions helped limit further activity while the investigation continued.
9. Investigation and Evidence Collection
The evidence collection section records the information used to investigate the incident.
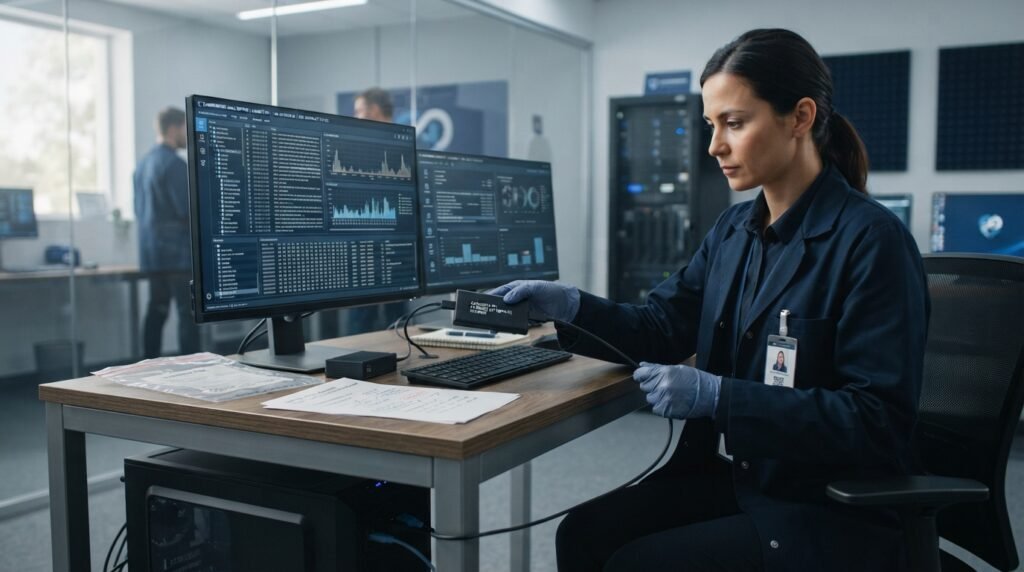
Possible evidence includes:
- Email headers and attachments.
- Firewall logs.
- System event logs.
- Endpoint security alerts.
- Network traffic records.
- Screenshots.
- File hashes.
- Disk and memory images.
- Login records.
- Application logs.
Keep an evidence register with the following details:
| Evidence ID | Evidence Description | Collection Date | Collected By | Storage Location |
|---|---|---|---|---|
| EV-001 | Suspicious email | Oct. 28, 2026 | Security Analyst | Restricted evidence folder |
| EV-002 | Endpoint security alert log | Oct. 28, 2026 | SOC Analyst | Secure log repository |
| EV-003 | Workstation disk image | Oct. 28, 2026 | Forensic Specialist | Encrypted evidence storage |
| EV-004 | Firewall activity log | Oct. 28, 2026 | Network Administrator | Restricted security archive |
The organization should protect collected evidence from unauthorized changes. Record who collected, accessed, or transferred each item.
This process is known as chain of custody.
Example 10:
A security analyst collected the suspicious email and saved it as EV-001. The original message was preserved, and a working copy was used for investigation.
This record helps show where the evidence came from and how the team handled it.
10. Recovery and Remediation Actions
Recovery means restoring affected systems and services to normal operation.
Remediation means fixing the security weakness that allowed the incident to happen.
Common actions include:
- Removing malicious software.
- Reinstalling affected operating systems.
- Restoring files from clean backups.
- Resetting compromised passwords.
- Installing security updates.
- Enabling MFA.
- Reviewing account permissions.
- Checking systems for signs of further compromise.
- Increasing security monitoring.
Example 11:
The IT team removed the malicious software and restored the affected workstation from a verified backup. The employee received a new password, and the security team enabled MFA for the account.
The report should state which actions were completed and which still need attention.
11. Business and Data Impact
This section explains how the incident affected the organization.
Include:
- Work interruptions.
- Financial losses or estimated recovery costs.
- Customer impact.
- Employee impact.
- Data exposure or loss.
- Service downtime.
- Legal or regulatory concerns.
If the team cannot confirm whether data was exposed, state that clearly.
Example 12:
The incident interrupted the finance employee’s work for approximately five hours. The initial investigation found no evidence that customer records were accessed or copied. The organization is continuing to review its security logs.
Avoid reporting estimated financial losses as confirmed figures. Clearly label estimates.
12. Lessons Learned and Preventive Actions
After resolving an incident, the organization should review what worked and what needs improvement.
The report should list specific actions, responsible people, and target dates.
| Recommended Action | Responsible Team | Priority | Target Date |
|---|---|---|---|
| Enable MFA for all employee accounts | IT Security | High | Nov. 10, 2026 |
| Improve email attachment filtering | IT Operations | High | Nov. 12, 2026 |
| Provide phishing awareness training | HR and Security | Medium | Nov. 20, 2026 |
| Review endpoint protection settings | Security Team | High | Nov. 8, 2026 |
| Test backup recovery procedures | IT Operations | Medium | Nov. 25, 2026 |
Example 13:
The review found that the company needed stronger email protection and wider MFA coverage. The security manager assigned both tasks to the IT department with target completion dates.
This turns the incident report into a practical improvement plan.
Complete Cybersecurity Incident Response Report Example
The following is a fictional but realistic ransomware incident response report. It shows how an organization can document a security event from detection to recovery.
All company names, dates, account details, and system names are fictional.
Sample Cybersecurity Incident Response Report
Report Information
| Field | Details |
|---|---|
| Organization | ABC Financial Services |
| Incident ID | SEC-2026-014 |
| Report Title | Ransomware Security Incident |
| Incident Type | Ransomware |
| Date Detected | October 28, 2026 |
| Detection Time | 9:15 AM ET |
| Severity | High |
| Current Status | Resolved |
| Report Prepared By | IT Security Manager |
| Department | Information Technology |
1. Executive Summary
On October 28, 2026, ABC Financial Services detected ransomware activity on an employee workstation in the finance department.
The incident was detected by endpoint security software after an employee opened a suspicious email attachment. The security team disconnected the affected workstation from the company network and started an investigation.
The investigation found no evidence of unauthorized access to the customer database. The affected workstation was cleaned and restored from a verified backup.
The incident was resolved, and the company assigned additional security improvements to the IT department.
2. Incident Description
An employee received an email that appeared to contain an invoice from a supplier. The employee opened the attached file at approximately 9:05 AM ET.
A few minutes later, endpoint security software detected unusual file activity and generated an alert.
The security team reviewed the alert and confirmed suspicious activity consistent with a ransomware infection.
3. Affected Systems
| System | Identifier | Status |
|---|---|---|
| Employee workstation | FIN-PC-014 | Infected |
| Finance user account | finance.user01 | Password reset |
| Company email | Microsoft 365 | Suspicious email removed |
| File server | FILE-SRV-02 | No confirmed impact |
| Customer database | CUSTOMER-DB-01 | No confirmed unauthorized access |
4. Incident Timeline
| Time (ET) | Activity |
|---|---|
| 9:05 AM | Employee opened suspicious attachment |
| 9:15 AM | Endpoint security alert generated |
| 9:22 AM | Security team confirmed suspicious activity |
| 9:30 AM | Workstation disconnected from network |
| 10:15 AM | Initial investigation completed |
| 12:00 PM | Malicious software removed |
| 2:30 PM | Workstation restored from backup |
| 3:00 PM | System checks completed |
5. Root Cause
The investigation found that the incident started after an employee opened a malicious email attachment.
The attachment launched an unauthorized program on the employee’s workstation. The investigation also identified that the employee account did not have MFA enabled.
The available evidence supported phishing as the initial entry method.
6. Containment Actions
The security team completed these actions:
- Disconnected the affected workstation from the company network.
- Reset the affected employee’s password.
- Removed the suspicious email from employee inboxes.
- Reviewed security alerts for related activity.
- Checked connected systems for signs of infection.
- Restricted access to the affected workstation during the investigation.
7. Evidence Collected
| Evidence ID | Description | Status |
|---|---|---|
| EV-001 | Original suspicious email | Preserved |
| EV-002 | Endpoint security alert logs | Collected |
| EV-003 | Workstation forensic image | Preserved |
| EV-004 | Firewall activity records | Collected |
All collected evidence was stored in a restricted security repository.
8. Business Impact
The incident affected one employee workstation in the finance department.
- One workstation was temporarily unavailable.
- Finance work was interrupted for approximately five hours.
- No customer database access was confirmed during the initial investigation.
- No confirmed customer data loss was identified.
- The organization restored the affected workstation from a verified backup.
9. Recovery Actions
The IT department completed the following recovery steps:
- Removed malicious software.
- Restored the workstation from a verified backup.
- Reset the employee’s account password.
- Checked the workstation for suspicious activity.
- Updated the affected system.
- Confirmed that the workstation could safely reconnect to the company network.
10. Preventive Actions
| Action | Assigned Team | Status |
|---|---|---|
| Enable MFA for all employee accounts | IT Security | Pending |
| Improve email attachment filtering | IT Operations | Pending |
| Conduct phishing awareness training | HR and Security | Pending |
| Review endpoint security policies | Security Team | In Progress |
| Test backup recovery procedures | IT Operations | Pending |
11. Final Assessment
The ransomware incident was contained and the affected workstation was restored.
The investigation identified a malicious email attachment as the initial entry method. The organization found no evidence of unauthorized access to its customer database during the investigation period.
The IT department was assigned preventive actions to reduce the risk of similar incidents.
12. Report Approval
| Role | Name | Approval |
|---|---|---|
| Report Prepared By | IT Security Manager | Pending |
| Reviewed By | Chief Information Security Officer | Pending |
| Approved By | IT Director | Pending |
This sample is for educational use. A real incident report should reflect verified evidence, actual response actions, and the organization’s reporting requirements.
How to Write a Cybersecurity Incident Response Report
You can follow these steps to prepare a clear and useful report for your organization.
Step 1: Collect Basic Incident Information
Start by recording the incident ID, date, detection time, incident type, and current status.
Speak with the person who reported the event and the team responsible for investigating it.
Step 2: Describe What Happened
Write a short explanation of the event.
Include how the incident started, how it was detected, and which systems were involved.
Use facts from security logs and investigation records. Do not present guesses as confirmed findings.
Step 3: Build an Incident Timeline
Record each important event in chronological order.
Include:
- When the incident started, if known.
- When the event was detected.
- When the response team was notified.
- When containment began.
- When the threat was removed.
- When recovery was completed.
Use the correct time zone for every entry.
Step 4: Identify Affected Systems
List the devices, accounts, applications, servers, and networks involved.
If an asset was checked but no impact was found, state that separately from confirmed affected assets.
Step 5: Record Response Actions
Document each action taken by the response team.
Include the person responsible, date, time, and result.
For example, record when an account was disabled or when an infected computer was isolated.
Step 6: Analyze the Root Cause
Review the available evidence to identify how the incident happened.
If the cause is still unknown, write Under Investigation rather than making an unsupported claim.
Step 7: Explain the Business Impact
Describe the effect on employees, customers, systems, and business operations.
Separate confirmed losses from estimates and possible impacts.
Step 8: Add Recovery and Prevention Plans
Explain how the organization restored its systems.
List the remaining security improvements, assign responsible teams, and set realistic deadlines.
Step 9: Review and Approve the Report
Ask the relevant security manager or authorized reviewer to check the report.
Confirm that the timeline, evidence, findings, and response actions are accurate.
Step 10: Store the Report Securely
A cybersecurity incident report may contain sensitive technical and business information.
Store it in a restricted location. Give access only to authorized people, and follow the organization’s document retention policy.
Common Mistakes to Avoid in a Cybersecurity Incident Report
Even a detailed report can be difficult to use if important information is missing or unclear.
Avoid these common mistakes.
1. Missing Dates and Times
A report without clear timestamps makes it difficult to reconstruct events.
Better approach: Record dates, times, and time zones for important actions.
2. Using Unconfirmed Information
Do not state that customer information was stolen if the investigation has not established that fact.
Better approach: Use clear labels such as Confirmed, Not Confirmed, and Under Investigation.
3. Leaving Out Evidence Details
A report should explain which evidence was collected and where it was stored.
Better approach: Use an evidence register with unique identification numbers.
4. Writing Too Much Technical Information for Managers
Senior managers may not understand every technical term in a security investigation.
Better approach: Give a simple executive summary and place detailed technical findings in a separate section or appendix.
5. Ignoring Business Impact
A report should explain more than what happened to a computer or server.
Better approach: Include work interruptions, affected departments, service downtime, and confirmed data exposure.
6. Failing to Assign Preventive Actions
A list of recommendations is not enough if nobody is responsible for completing them.
Better approach: Assign an owner, priority, and target date to every improvement task.
Best Practices for Cybersecurity Incident Reporting
Use these practices to improve the quality of your reports.
- Use a standard template: Keep the same basic report structure for different incident types.
- Record events as they happen: Do not wait until the investigation ends to write down important actions.
- Protect sensitive information: Restrict access to reports and evidence.
- Keep evidence unchanged: Preserve original records and document evidence handling.
- Separate facts from opinions: Clearly identify confirmed findings and open questions.
- Use clear language: Explain technical terms in words that managers and other readers can understand.
- Review the response: Record what worked and what needs improvement.
- Track follow-up actions: Check whether assigned security improvements are completed.
- Update reports when needed: Record important changes in scope, impact, and incident status.
A useful report should give technical teams enough detail to investigate the event while helping managers make informed decisions.
Cybersecurity Incident Response Report Template
You can copy the following cybersecurity incident report template and use it as a starting point for your organization.
Replace the sample fields with information from your actual investigation.
1. Report Information
- Organization Name:
- Incident ID:
- Incident Title:
- Incident Type:
- Date Detected:
- Time Detected:
- Date Reported:
- Severity Level:
- Current Status:
- Report Prepared By:
- Incident Manager:
2. Executive Summary
- What happened?
- How was the incident detected?
- Which systems were affected?
- What was the business impact?
- What actions were taken?
- What is the current status?
3. Incident Description
- Detailed description:
- Initial detection method:
- Suspected entry point:
- Confirmed attack method:
- Affected departments:
4. Affected Systems
- System Name:
- Hostname:
- IP Address:
- Operating System:
- Account or User ID:
- Impact:
- Current System Status:
5. Incident Timeline
| Date and Time | Event | Action Taken | Responsible Person |
|---|---|---|---|
6. Severity and Risk Assessment
- Severity Level:
- Confidentiality Impact:
- Integrity Impact:
- Availability Impact:
- Business Impact:
- Recovery Difficulty:
7. Root Cause Analysis
- Confirmed Root Cause:
- Contributing Factors:
- Security Weakness:
- Investigation Findings:
- Unresolved Questions:
8. Containment Actions
- Action Taken:
- Date and Time:
- Responsible Person:
- Result:
9. Evidence Collection
| Evidence ID | Evidence Description | Collection Date | Collected By | Storage Location |
|---|---|---|---|---|
10. Recovery and Remediation
- Malware Removal:
- Password Resets:
- System Restoration:
- Security Updates:
- Backup Verification:
- Recovery Completion Date:
11. Business Impact
- Affected Departments:
- Service Downtime:
- Customer Impact:
- Data Exposure:
- Estimated Financial Impact:
- Additional Risks:
12. Preventive Actions
| Action Required | Responsible Person | Priority | Deadline | Status |
|---|---|---|---|---|
13. Final Assessment
- Incident Resolution Summary:
- Final Investigation Findings:
- Remaining Risks:
- Follow-Up Requirements:
14. Approval
- Prepared By:
- Reviewed By:
- Approved By:
- Approval Date:
FAQs About Cybersecurity Incident Response Reports
1. What is a cybersecurity incident response report?
A cybersecurity incident response report is a document that records a security event, its impact, investigation findings, and the actions taken to contain and resolve it.
2. What is an example of a cybersecurity incident report?
A ransomware report is a common example. It may explain how an employee opened a harmful email attachment, how the security team detected the infection, which computer was affected, and how the team restored the system.
3. What should a cybersecurity incident response report include?
It should include the incident details, executive summary, timeline, affected systems, severity level, root cause, evidence, containment actions, recovery steps, business impact, and preventive actions.
4. Who is responsible for writing an incident response report?
The IT security team, Security Operations Center (SOC), or assigned incident response manager usually prepares the report. Other team members may provide investigation details and review the final document.
5. How long should a cybersecurity incident report be?
There is no fixed length. A simple incident may need only a few pages, while a major data breach or ransomware attack may require a longer report with technical records and evidence.
The report should contain all relevant information without adding unnecessary details.
6. What is the difference between an incident report and an incident response plan?
An incident report records a security event that has happened and explains how the organization handled it.
An incident response plan explains what an organization should do if a security incident occurs.
The plan guides the response, while the report documents the event and the actions taken.
7. Should an incident response report include evidence?
Yes. A report should identify relevant evidence, explain when and how it was collected, and record where it is stored.
Examples include security logs, suspicious emails, screenshots, file hashes, and forensic images.
8. What are the four main stages of incident response?
A simple response process can include:
- Preparation: Set up security tools, response roles, and procedures.
- Detection and analysis: Identify the event and investigate its scope.
- Containment, eradication, and recovery: Limit the damage, remove the threat, and restore affected systems.
- Post-incident review: Review the response and plan security improvements.
These are common stages in traditional incident response guidance. Current NIST guidance also places incident response within broader cybersecurity risk management.
9. What is the difference between a security incident and a data breach?
A security incident is an event that affects or threatens the security of systems or information.
A data breach involves unauthorized access to, disclosure of, or exposure of protected information.
A security incident does not always result in a confirmed data breach.
10. Can small businesses use a cybersecurity incident response report template?
Yes. Small businesses can use a simple template to record security events, affected systems, response actions, and recovery steps.
They can add technical details as needed and assign a responsible person to each follow-up task.
Conclusion
A cybersecurity incident response report gives an organization a clear record of a security event and how it was handled. It helps IT teams review the incident, identify its root cause, measure business impact, and improve security procedures.
The ransomware example in this guide shows how to document an incident from initial detection to final recovery. The reusable template can also help businesses create consistent reports for phishing attacks, malware infections, unauthorized access, and data breaches.
Use a standard report format, record accurate timestamps, preserve evidence, and assign clear owners to preventive actions. A good report should explain what happened, what was done, and what the organization needs to improve next.
Emily Carter (Content Writer & Communication Specialist) is a content writer and communication specialist at AllTypeInfo.com. She writes clear, practical, and easy-to-follow guides on email responses, message replies, writing templates, and everyday communication tips. Her goal is to help readers communicate with confidence in both personal and professional settings.